Palo Alto Networks GlobalProtect Authentication Bypass: What Security Teams Should Know About CVE-2026-0257
Background
Palo Alto Networks GlobalProtect is widely used by enterprises to provide secure remote access to internal systems and applications. Because VPN gateways often sit at the edge of corporate networks, vulnerabilities in these systems can quickly become high-priority risks for security teams.
On May 13, 2026, Palo Alto Networks disclosed CVE-2026-0257, an authentication bypass vulnerability affecting the GlobalProtect portal and gateway components of PAN-OS and certain Prisma Access deployments. The vulnerability allows a remote, unauthenticated attacker to bypass GlobalProtect authentication and establish an unauthorized VPN connection when specific configuration conditions are present.
Although the issue was initially rated as medium severity, the risk profile changed quickly after exploitation was observed in the wild. On May 29, 2026, CISA added CVE-2026-0257 to its Known Exploited Vulnerabilities catalog, and Palo Alto Networks updated the advisory to reflect higher urgency.
For organizations that rely on GlobalProtect for remote access, this vulnerability is important not only because of the technical flaw, but also because of where it exists: at the boundary between the public internet and the internal enterprise network.
Why This Vulnerability Matters
CVE-2026-0257 affects GlobalProtect deployments where authentication override cookies are enabled together with a vulnerable certificate configuration.
Authentication override cookies are designed to improve user experience by allowing users to reconnect without repeatedly entering credentials. In a secure implementation, these cookies must be strongly protected and validated so that only cookies legitimately issued by the server are trusted.
In vulnerable configurations, GlobalProtect may accept a forged authentication cookie as valid. This can allow an attacker to impersonate a user and authenticate to the VPN without knowing the user’s password.
The practical impact is significant. A successful attacker may be able to:
- Establish an unauthorized VPN session
- Gain access to internal network resources reachable from the VPN
- Impersonate a legitimate user account
- Use the VPN connection as a starting point for further internal reconnaissance or lateral movement
Affected Products and Conditions
According to Palo Alto Networks, CVE-2026-0257 affects certain PAN-OS and Prisma Access versions when a GlobalProtect portal or gateway is configured and authentication override cookies are enabled under the vulnerable certificate configuration.
Administrators can verify whether authentication override cookies are enabled in the GlobalProtect portal and gateway settings by checking whether “Generate cookie for authentication override” or “Accept cookie for authentication override” is enabled.
Affected products include PAN-OS 10.2, 11.1, 11.2, and 12.1 branches, as well as Prisma Access deployments running affected 10.2 and 11.2 releases. Panorama and Cloud NGFW are not impacted by this vulnerability.
Because the fixed versions differ across software branches and maintenance releases, organizations should verify their exact version against the official Palo Alto Networks security advisory rather than relying solely on the major release number. Palo Alto Networks maintains the latest affected-version and remediation information here.
What Security Teams Should Look For
Because this vulnerability affects VPN authentication, security teams should review both configuration and authentication activity.
Important signs to investigate include:
- GlobalProtect logins using cookie-based authentication from unfamiliar source IP addresses
- Authentication attempts to privileged or local administrator accounts
- Successful VPN logins from hosting providers, cloud infrastructure, or unexpected geographies
- Unusual GlobalProtect client metadata, such as generic hostnames or unexpected operating system details
- VPN sessions created outside normal business hours or from unusual locations
- New VPN-assigned IP addresses associated with suspicious authentication events
These signals are especially important for internet-facing GlobalProtect portals and gateways. Even if no lateral movement is immediately observed, any suspicious successful VPN authentication should be investigated as a potential initial access event.
RidgeBot Detection
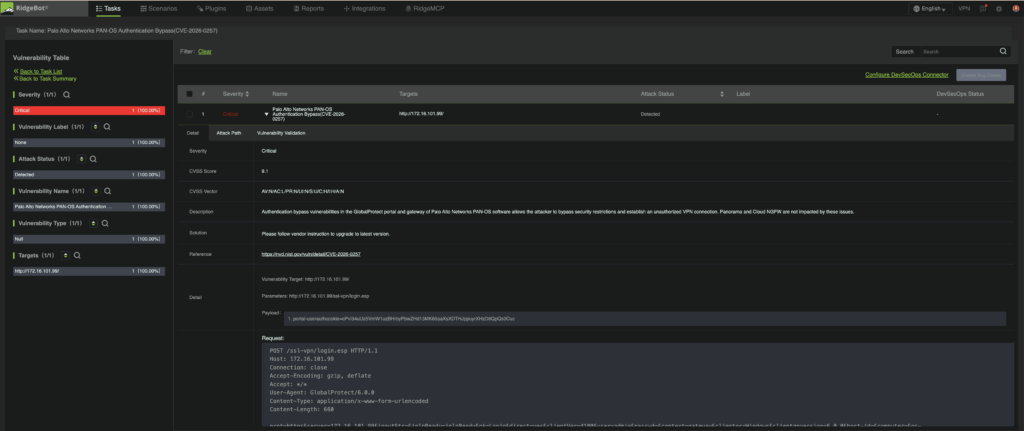
RidgeBot automatically detects CVE-2026-0257 by validating exploitability against the target instead of relying only on passive version checks or banner matching.
At a high level, RidgeBot first verifies that the target is a GlobalProtect service. It then performs a controlled validation of the authentication bypass behavior by checking whether the service accepts a specially crafted authentication cookie in a way that indicates the vulnerable configuration is present.
Recommended Mitigation
The primary remediation is to upgrade affected PAN-OS and Prisma Access deployments to the fixed versions provided by Palo Alto Networks.
Security teams should:
- Upgrade all GlobalProtect portals and gateways that generate or accept authentication override cookies, including both internal and external components.
- For hybrid Prisma Access deployments, upgrade all on-premises NGFWs to the fixed PAN-OS versions to maintain cookie compatibility with Prisma Access.
- Avoid leaving the environment partially upgraded for long periods, as mixed versions may cause authentication cookie compatibility issues.
- If authentication override cookies are not required, disable them to reduce exposure.
- Review GlobalProtect authentication logs for suspicious cookie-based logins, unusual VPN sessions, privileged account usage, or access from unfamiliar IP addresses.
For phased upgrades, Palo Alto Networks provides a temporary compatibility option for mixed-version environments. Once all components are upgraded, strict cookie validation should be re-enabled to fully apply the security fix.
Conclusion
CVE-2026-0257 is a serious authentication bypass vulnerability in Palo Alto Networks GlobalProtect. While the vulnerability depends on specific configuration conditions, the affected feature is common enough that exposed organizations should treat it as an urgent patching priority.
The risk is amplified by the role GlobalProtect plays in enterprise environments. VPN gateways are often trusted access points into internal networks, and an authentication bypass at this layer can give attackers a direct path into sensitive systems.
Organizations running affected PAN-OS or Prisma Access versions should upgrade immediately, verify their authentication override cookie configuration, and review VPN authentication logs for signs of suspicious activity.
RidgeBot helps security teams validate CVE-2026-0257 exposure safely and automatically, enabling defenders to identify exploitable systems quickly and prioritize remediation based on real risk.
by